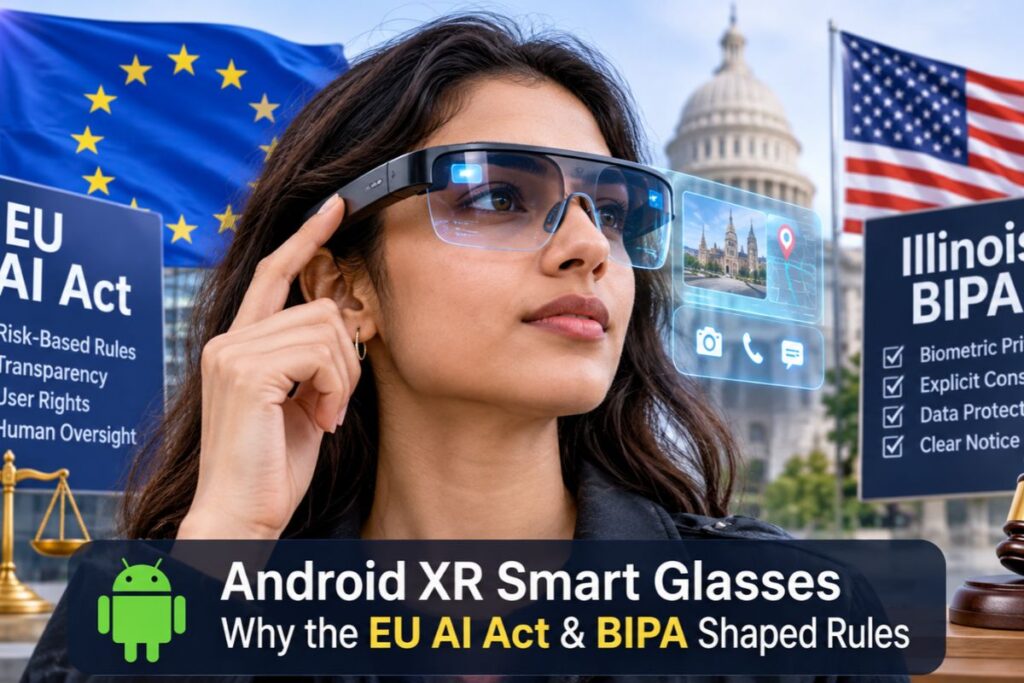
Google banned real-time facial recognition and added automatic face-blurring on Android XR smart glasses to neutralize binding legal liability in Europe and the United States. The rules shield Google from EU AI Act fines up to €35 million, or 7% of global revenue, and prevent repeat class-action lawsuits under Illinois’s biometric privacy law, which has already cost Google over $108 million.
What Legal Triggers Do Google’s Android XR Privacy Rules Remove?
Google’s Android XR privacy rules strip facial geometry locally on the paired phone before Gemini processes an image, preventing Google’s servers from collecting or storing biometric identifiers without consent.
When Google published its privacy commitments for Android XR smart glasses on November 12, 2026, the company paired three technical and policy rules: automatic face redaction before images reach its Gemini assistant, immediate deletion of Gemini camera frames, and a ban on real-time facial identification in its Android XR App Quality Guidelines.
Stripping faces locally on the paired smartphone, as Google confirmed in launch clarifications, ensures Google never ingests facial geometry, which consists of the mathematical measurements of a person’s facial structure used to verify identity. In its Intelligent Eyewear Security and Privacy Commitments, Google states that building privacy protections for both wearers and bystanders is required to earn user trust before launching camera-equipped eyewear into public spaces.
How Does EU AI Act Article 5 Penalize Untargeted Biometric Capture?
EU AI Act Article 5 prohibits untargeted facial scraping, workplace emotion inference, and biometric categorization, carrying fines up to €35 million or 7% of worldwide annual turnover.
In Europe, launching smart glasses capable of identifying bystanders collides directly with Regulation (EU) 2024/1689, known as the European Union Artificial Intelligence Act (EU AI Act), which is Europe’s comprehensive risk-based law governing artificial intelligence. The law’s outright prohibitions under Article 5 took effect on February 2, 2025, and its administrative fine schedule became enforceable on August 2, 2025.
Under the EU AI Act penalty framework, violations of Article 5 trigger penalties of up to €35 million or 7% of a company’s total worldwide annual turnover, whichever is higher. Three specific Article 5 bans restrict wearable biometric tools:
- Article 5(1)(e): Prohibits placing on the market or using AI systems that create or expand facial-recognition databases through the untargeted scraping of facial images from the internet or closed-circuit television footage.
- Article 5(1)(f): Prohibits AI systems that infer emotions of people in workplaces and educational institutions, except for medical or safety reasons.
- Article 5(1)(g): Prohibits biometric categorization systems that classify individuals based on biometric data to deduce race, political opinions, trade union membership, religious beliefs, or sexual orientation.
Beyond the AI Act, Article 9 of the European Union’s General Data Protection Regulation (GDPR) classifies biometric data used to uniquely identify a person as a special category of personal data, requiring explicit consent before processing, a condition unworkable for strangers walking past a camera lens.
How Much Has Illinois’s BIPA Cost Google in Biometric Lawsuits?
Google has paid more than $108 million across Illinois Biometric Information Privacy Act (BIPA) class-action settlements, including $100 million over Google Photos and $8.75 million over Google Workspace for Education, creating direct financial pressure to block unconsented bystander face capture.
In the United States, Google’s wearable privacy design follows a series of costly payouts under Illinois’s Biometric Information Privacy Act (740 ILCS 14), known as BIPA, which is an Illinois state law requiring companies to obtain written informed consent before collecting biometric identifiers. Under Section 15(b) of BIPA, a private entity cannot collect, capture, or obtain a scan of face geometry without first informing the subject in writing and receiving a written release.
Section 20 of BIPA allows private plaintiffs to recover $1,000 per negligent violation and $5,000 per intentional or reckless violation. According to biometric legal compliance analyses, BIPA is the only U.S. state biometric statute granting individuals a private right to sue without proving actual financial injury.
Google’s settled Illinois BIPA liabilities include:
- $100 million (2022): Paid to settle Rivera v. Google LLC, an Illinois class-action lawsuit alleging Google Photos collected and stored facial-geometry templates without prior written consent.
- $8.75 million (approved October 2025, paid out February 2026): Paid to settle H.K. et al. v. Google LLC (Case No. CC 20LL00017), resolving claims that Google Workspace for Education collected voiceprints and face-geometry templates from Illinois schoolchildren.
In October 2025, Google also reached a confidential settlement in an Illinois BIPA lawsuit over open-source facial-recognition training datasets. Earlier that year, in May 2025, Google agreed to a $1.375 billion privacy settlement with the Texas Attorney General that resolved claims under Texas’s Capture or Use of Biometric Identifier Act (CUBI) alongside geolocation tracking allegations.
Why Did Google Diverge From Meta on Smart Glasses Facial Recognition?
Unlike Meta’s U.S.-centric consumer focus on Ray-Ban smart glasses, Google and Samsung are positioning Android XR smart glasses for global and enterprise workplace deployments where unconsented biometric capture violates corporate and European compliance rules.
Much of the initial coverage attributed Google’s restrictions to the 2013 backlash against the original Google Glass and contrasted Google’s stance with Meta, which has explored adding facial-recognition features to its Ray-Ban smart glasses. That contrast also reflects different commercial targets and geographic exposure.
Google and hardware partner Samsung are launching Android XR smart glasses first in the United States and South Korea on December 10, 2026, while integrating the platform into Android Enterprise management and Google Intelligent Endpoints for workplace use. According to Samsung’s enterprise XR documentation, corporate IT buyers require strict endpoint security and granular camera controls before deploying spatial hardware inside regulated offices and healthcare facilities.
At the same time, advocates for blind and low-vision users, and proponents of Meta’s facial-recognition explorations, note that real-time person identification can serve as a practical memory and accessibility aid for people with face blindness or visual impairments, a utility that blanket platform bans foreclose.
What Does Google’s Legal Shield Cover, and Leave Open?
Google’s local Gemini redaction shields its own cloud servers from storing biometric identifiers, but enforcing the facial-recognition ban through Google Play Store policy leaves third-party CameraX streams unblurred on the paired phone.
By running face redaction locally on the paired phone inside the Gemini pipeline and discarding Gemini camera frames immediately, Google avoids receiving or storing raw bystander facial geometry in its cloud. In its November 12, 2026 announcement, Google also committed to physical power switches, outward-facing recording lights with tamper sensors, and refusing to use Gemini visual data for ad targeting or AI model training, measures that go beyond bare statutory minimums.
Yet as Biometric Update’s technical analysis of Google’s developer documentation points out, Google’s ban on facial recognition relies on Google Play Store policy rather than a universal operating-system block on the camera stream. Third-party apps on Android companion phones can bind to the glasses’ camera via Android’s CameraX (ImageAnalysis) interface, Android’s standard programming interface for live camera frame analysis, after requesting runtime permission (ProjectedActivityCompat), receiving unblurred video frames on the device while leaving enforcement against non-Play sideloaded apps unresolved.
Frequently Asked Questions
Why did Google ban real-time facial recognition on Android XR smart glasses? Google banned real-time facial recognition and added local face-blurring for Gemini to prevent violations of EU AI Act Article 5, which carries fines up to €35 million or 7% of global annual turnover, and to avoid repeat class-action lawsuits under Illinois’s Biometric Information Privacy Act (BIPA).
How much has Google paid in Illinois BIPA biometric privacy lawsuits? Google has paid more than $108 million across Illinois BIPA class-action settlements, including $100 million in 2022 to settle Rivera v. Google LLC over Google Photos face grouping and $8.75 million in H.K. et al. v. Google LLC over Google Workspace for Education student voiceprints and face templates.
When do EU AI Act facial recognition prohibitions take effect? Under Regulation (EU) 2024/1689, the EU AI Act’s outright prohibitions under Article 5, including bans on untargeted facial scraping and workplace emotion inference, took effect on February 2, 2025, with administrative fines becoming enforceable on August 2, 2025.
Does Google’s face-blurring block third-party Android XR apps from seeing faces? No. Local face redaction runs only inside Google’s Gemini pipeline on the paired phone, while third-party apps granted runtime camera permission (ProjectedActivityCompat) can access unblurred video frames through Android’s CameraX (ImageAnalysis) interface, with facial recognition barred through Google Play Store policy rather than an operating-system block.
Praseetha K
Praseetha K is the Managing Editor of Clarity Times. She edits, verifies and publishes the newsroom's articles, and also writes analysis on policy, law, business and technology. Articles she writes are edited by the Editor-in-Chief before publication.