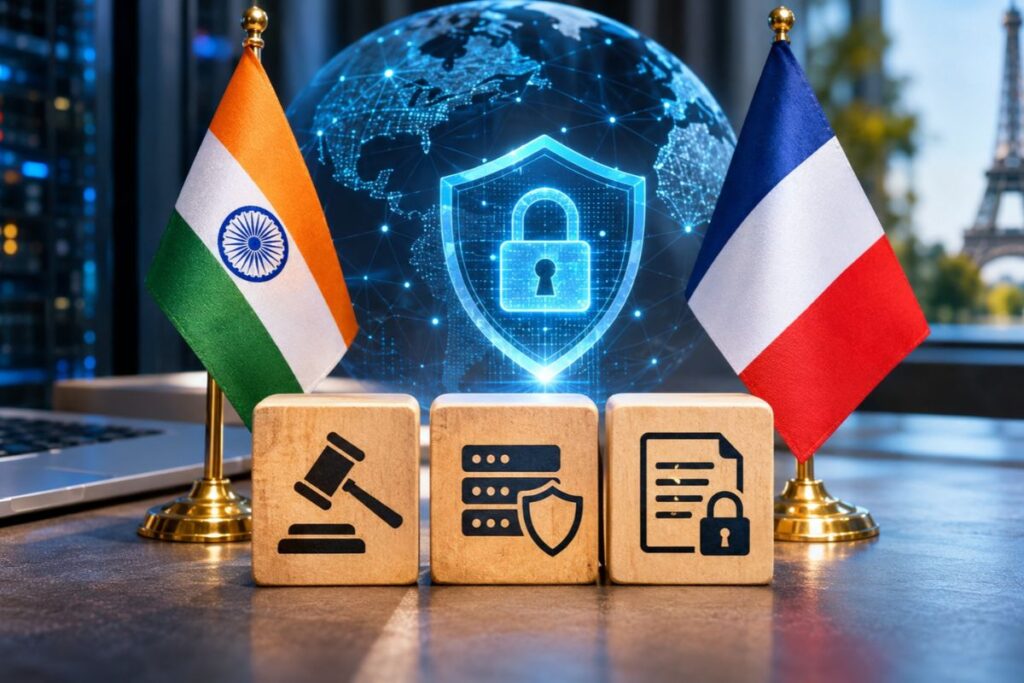
India-France cybersecurity cooperation cannot immediately produce live threat-intelligence sharing or mutual product certification because domestic and European laws clash on three points: India lacks European Union data-privacy adequacy, breach-reporting deadlines collide at six hours versus 24 hours, and both governments mandate separate domestic security testing before tech gear can be sold.
Readouts from the November 9–10, 2026 Paris talks led by Indian Foreign Secretary Vikram Misri and French Foreign Ministry Secretary-General Martin Briens pledged closer work under the inaugural India-France Economic Security and Critical Technologies Dialogue. Yet diplomats cannot waive binding statutes.
Why Can’t France Strike a Bilateral Cyber Deal With India?
France cannot sign a standalone cyber-integration treaty with New Delhi because French cyber regulation is legally bound to European Union single-market law.
In France, national cyber defense rests with the Agence nationale de la sécurité des systèmes d’information (ANSSI), the government agency that protects state networks and oversees critical infrastructure security. Under the French Defense Code and European Union Directive 2022/2555. known as the NIS2 Directive, the EU-wide law setting baseline cybersecurity and incident-reporting standards. ANSSI must follow Brussels-level rules on data handling and supervision.
India divides its cyber authority across two statutory agencies under the Information Technology Act, 2000. Section 70A designates the National Critical Information Infrastructure Protection Centre (NCIIPC) to guard vital networks, while Section 70B empowers the Indian Computer Emergency Response Team (CERT-In). India’s national agency for tracking and responding to cyberattacks, and to issue binding security rules.
Under ANSSI’s operational cyberdefense regulations, technical incident records containing victim identifiers qualify as regulated personal data, barring cross-border transfers outside approved European legal mechanisms.
How Does India’s Lack of EU GDPR Adequacy Block Threat-Intelligence Sharing?
Because raw cyber-threat feeds contain internet protocol (IP) addresses and device identifiers classified as personal data in Europe, French agencies cannot legally transfer them freely to India without an EU adequacy ruling.
Real-time cyber defense relies on exchanging technical indicators such as suspicious IP addresses, server logs, and hardware identifiers under the European Union General Data Protection Regulation (GDPR). Europe’s comprehensive privacy law governs personal data. Those technical markers count as personal data whenever they can be linked back to an individual user or employee.
Under GDPR Article 45, European public agencies and companies may transfer personal data freely only to countries the European Commission has formally declared “adequate.” As of November 2026, the European Commission’s official adequacy registry includes Japan, the United Kingdom, South Korea, and Brazil. does not include India.
India enacted its Digital Personal Data Protection (DPDP) Act in August 2023 and notified its implementing rules in November 2025, with full compliance scheduled for May 2027. However, Section 17(2) of the DPDP Act lets India’s central government exempt state agencies from the law on grounds of sovereignty, state security, and public order.
Legal analysts tracking India-EU data adequacy note that broad executive exemptions without independent judicial oversight remain a core barrier for European regulators evaluating privacy equivalence. Private companies rely on European Commission Standard Contractual Clauses (SCCs). Pre-approved legal contracts for commercial data transfers. Those commercial agreements do not authorize agency-to-agency intelligence feeds between ANSSI and CERT-In.
How Do CERT-In’s 6-Hour Breach Rules Clash With French NIS2 Deadlines?
Companies operating in both jurisdictions face a direct statutory collision during a cyberattack: Indian law demands incident reports within six hours, whereas French law under the EU NIS2 Directive sets a 24-hour early-warning window.
Under CERT-In’s April 28, 2022 Cyber Security Directions, issued under Section 70B(6) of the Information Technology Act, covered service providers, data centers, and corporate entities must report specified cyber incidents within 6 hours of noticing them and store system logs inside India for 180 days. Following the Jan Vishwas (Amendment of Provisions) Act, 2023, non-compliance carries maximum fines of ₹1 crore, up from ₹1 lakh.
French operators follow a separate clock under Article 23 of the EU NIS2 Directive. Covered organizations must file an initial early warning with ANSSI within 24 hours of detecting a significant incident, followed by a formal incident notification within 72 hours.
In India, financial and market firms also answer to domestic sector clocks, including the Reserve Bank of India’s November 5, 2026 Master Directions on Cyber Resilience for non-bank payment operators. These require reporting unusual incidents within six hours. and the Securities and Exchange Board of India’s Cybersecurity and Cyber Resilience Framework. Incident-response teams straddling Paris and Bengaluru must submit preliminary disclosures in New Delhi hours before European forensic validation finishes, while ensuring Indian-resident log mandates do not trigger unauthorized transfers of EU employee data.
Why Must French and Indian Tech Gear Pass Separate Security Tests?
Hardware and software firms cannot sell across both markets on a single security certificate because India requires domestic laboratory testing under MTCTE while France enforces European CE-mark rules under the EU Cyber Resilience Act.
In India, the Department of Telecommunications enforces the Mandatory Testing and Certification of Telecom Equipment (MTCTE) regime, India’s compulsory pre-sale safety and security screening for network hardware. Under the National Centre for Communication Security’s ComSec scheme, routers, Wi-Fi customer gear, and optical network terminals must pass evaluation inside accredited Indian laboratories before sale.
According to compliance consultancy C-PRAV, NCCS security testing takes 8 to 10 weeks per device model and carries administrative fees of ₹10,000 to ₹50,000 on top of private lab charges. Separately, Indian government procurement relies on audits by the Standardisation Testing and Quality Certification (STQC) directorate.
New Delhi’s security establishment treats domestic lab testing and source-code scrutiny as essential defenses against supply-chain tampering across contested borders.
Europe enforces its own conformity regime under the EU Cyber Resilience Act (Regulation (EU) 2024/2847), the EU law requiring hardware and software with digital elements to meet baseline security and vulnerability-patching standards before receiving a European CE mark.
Both countries belong to the international Common Criteria Recognition Arrangement, where India serves as an authorizing nation up to Evaluation Assurance Level 4. However, Europe has adopted the harmonized EU Cybersecurity Certification Scheme on Common Criteria (EUCC). Europe’s unified certification system for high-assurance digital products. under which ANSSI issues EU-wide certificates for secure chips and smartcards. A French-certified firewall cannot skip Indian lab queues, and an Indian software product still requires separate European conformity assessments.
Why Paris and New Delhi Launched the Dialogue Anyway
The November 9–10, 2026 Paris meeting followed Indian Prime Minister Narendra Modi’s June 2026 visit to France and the bilateral Horizon 2047 roadmap. According to official diplomatic readouts, both governments aim to double bilateral trade within five years from a baseline of roughly €13.6 billion ($15 billion).
Even without statutory harmonization, the dialogue establishes an institutional channel for joint research fellowships under the 2026 Year of Innovation and political coordination on supply-chain vulnerabilities.
What Would Have to Change to Make Interoperability Real?
Turning diplomatic alignment into working cyber integration requires formal legal instruments rather than joint statements:
- Data-transfer adequacy: The European Commission would need to grant India a GDPR Article 45 adequacy decision. A review is unlikely to conclude before India’s Digital Personal Data Protection Act reaches full enforcement in May 2027.
- Mutual Recognition Agreements (MRAs): Brussels and New Delhi would have to negotiate a formal MRA through the EU-India Trade and Technology Council Working Group 1 so accredited labs in one jurisdiction can certify products for the other.
- Restricted agency protocols: ANSSI and CERT-In would need a narrow, bilateral protocol under the Traffic Light Protocol (TLP) standard. An international system for labeling how sensitive threat intelligence may be shared. Covering anonymized indicators stripped of personal data.
Until Brussels and New Delhi bridge those statutory gaps, French and Indian cyber agencies will remain bound by domestic rules that stop at their borders.
Related reporting: Read our analysis on the multi-million-dollar commercial zero-day exploit market and why India-Romania 2026 bilateral accords remain on paper.
Frequently Asked Questions
Why can’t ANSSI and CERT-In share live cyber threat intelligence automatically?
Under the EU General Data Protection Regulation (GDPR), technical threat indicators such as IP addresses and device identifiers qualify as personal data whenever they can be linked to an individual. Because India is not on the European Commission’s GDPR Article 45 adequacy registry as of November 2026, the French agency ANSSI cannot freely transfer raw personal data to CERT-In without an EU-level adequacy decision or a specialized anonymized sharing protocol.
How do cyber incident reporting deadlines differ between India and France?
Under CERT-In’s April 2022 Cyber Security Directions, covered organizations in India must report cyber incidents within 6 hours of noticing them, with non-compliance fines reaching ₹1 crore under the Jan Vishwas Act, 2023. In France, entities regulated under the EU NIS2 Directive have 24 hours to submit an initial early warning to ANSSI and 72 hours for a formal incident notification.
Does an EU cybersecurity certification allow French tech products to be sold in India without re-testing?
No, because India’s Department of Telecommunications requires network equipment such as routers and Wi-Fi gear to undergo security evaluation inside accredited Indian laboratories under the MTCTE ComSec scheme before sale. According to compliance firm C-PRAV, that domestic testing process takes 8 to 10 weeks per device model, regardless of existing European or Common Criteria certifications.
Can France negotiate a bilateral mutual recognition agreement for tech testing with India on its own?
No, because product conformity standards and data-protection rules are governed at the European Union level under the single market. Any formal Mutual Recognition Agreement allowing Indian and European testing laboratories to accept each other’s security certifications must be negotiated between New Delhi and the European Commission, such as through the EU-India Trade and Technology Council.
Praseetha K
Praseetha K is the Managing Editor of Clarity Times. She edits, verifies and publishes the newsroom's articles, and also writes analysis on policy, law, business and technology. Articles she writes are edited by the Editor-in-Chief before publication.