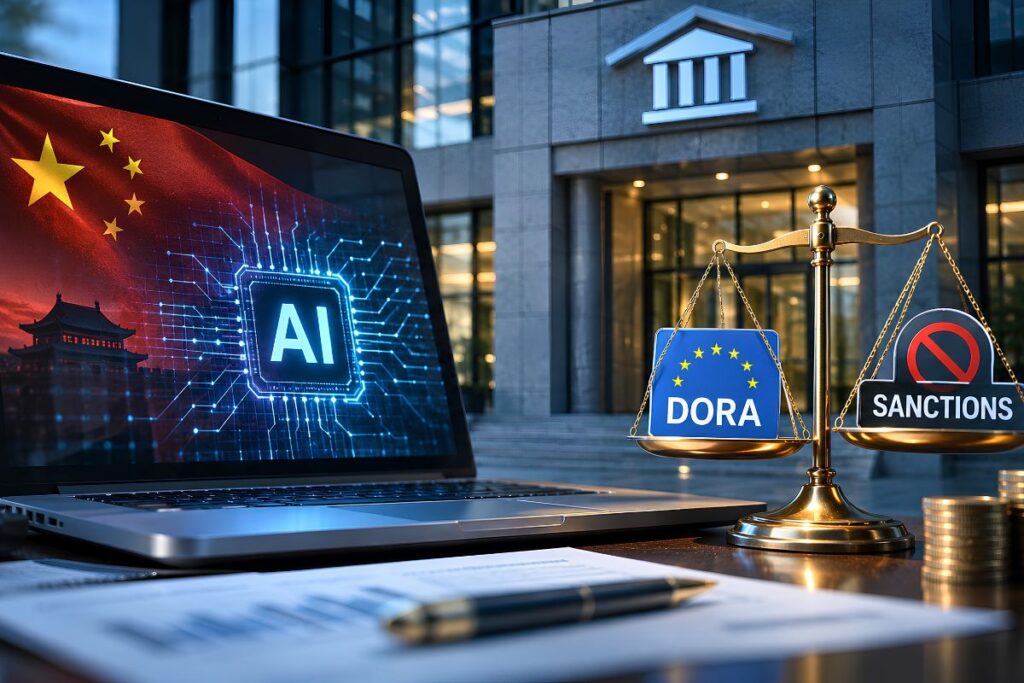
The primary risks of Chinese AI models in banking center on regulatory non-compliance under operational resilience laws, trade sanctions extending from silicon to model weights, and deep architectural lock-in. While local hosting isolates code execution, fine-tuning and workflow coupling force an emergency rewrite if geopolitical sanctions or sovereign banking mandates disqualify the underlying model family.
Fintech Procurement Cycle: 2014 vs. 2026
| Dimension | 2014: Telecom Hardware | 2026: Open-Weight Models |
|---|---|---|
| Vendor / Architecture | Huawei / ZTE | GLM / Qwen |
| Commercial Pitch | 40% cheaper gear | 90% cheaper tokens |
| Operational Thesis | “Boxes sit in domestic DCs” | “Weights run on local VPCs” |
| Regulatory Trigger | Telecoms (Security) Act 2021 | DORA Art. 28–30 / BIS EAR |
| Downstream Impact | £500M+ write-downs (BT, Vodafone) | $10M+ code refactoring run |
Why Is Migrating Away From an Open-Weight Model So Difficult?
Replacing an open-weight foundation model, a neural network whose numerical parameters are publicly downloadable rather than locked behind an external provider’s API, is an architectural overhaul rather than a simple configuration change. When engineering teams build software with an AI coding model, the surrounding developer toolchain adapts to that model family’s specific tokenization rules, output schemas, and context conventions.
Over months of deployment, internal prompt templates, automated test-generation suites, and code-review linters become tightly coupled to the base model’s quirks. Moving from a Chinese open-weight architecture like Zhipu AI’s GLM or Alibaba Cloud’s Qwen to a Western alternative such as Meta’s Llama or Mistral AI requires teams to rewrite prompt-routing layers, recalibrate inference parameters, and re-run regression audits across existing repositories.
Engineers frequently implement abstraction layers like vLLM or LiteLLM to maintain OpenAI-compatible API endpoints. While these proxies allow infrastructure teams to switch network addresses quickly, they do not resolve deeper software dependencies: proprietary system instructions, specialized fine-tuned checkpoints, and context-window optimizations fail to carry over cleanly between competing model families.
What Does the Huawei 5G Ban Teach Us About Foreign Infrastructure?
The corporate rationale behind adopting foreign open-weight models mirrors the strategy European telecommunications carriers used a decade ago. Between 2012 and 2018, mobile operators across the continent deployed network hardware from Chinese vendors such as Huawei Technologies Co., Ltd. and ZTE Corporation because the gear was cheaper, technically mature, and operated directly by domestic network engineers.
Carriers maintained that physical deployment inside domestic cell towers and regional data centers neutralized sovereign intelligence concerns. National security policy, however, reversed corporate procurement plans. Following updated geopolitical risk assessments, the United Kingdom Parliament enacted the Telecoms (Security) Act 2021, and the European Commission implemented the EU 5G Cybersecurity Toolbox.
The policy reversal triggered substantial balance-sheet penalties:
- According to regulatory disclosures from BT Group plc, removing Huawei hardware from its core mobile network cost the company £500 million.
- Vodafone Group Plc reported approximately €200 million in direct capital expenditures to strip out core network components across its European operations.
- Across the United Kingdom and continental Europe, total telecommunications spending reached billions of pounds as carriers diverted capital budgets from broadband expansion into retroactive equipment replacement.
The telecommunications sector established that maintaining physical custody of a technical asset offers no legal immunity once national security authorities alter foreign technology dependencies.
Can Export Controls and Sanctions Expand From Computer Chips to Software Weights?
Western trade restrictions are moving beyond physical computing equipment toward foundational software assets. While initial export controls targeted physical silicon manufacturing equipment and advanced graphic processing units (GPUs), international trade compliance regimes now examine downstream dual-use software distributions.
The United States Department of Commerce, through its Bureau of Industry and Security (BIS), manages the Export Administration Regulations (EAR), which place restrictions on foreign entities and dual-use technologies. Emerging regulatory frameworks are actively addressing advanced computing metrics, model parameters, and open-weight AI frameworks.
Supporters of open-weight systems emphasize an important physical boundary: static mathematical weights stored on local drives cannot query external command servers or execute unauthorized remote updates. Unlike telecom base stations running proprietary firmware, downloaded neural weights remain static files.
Even without outbound data connections, trade sanctions can prohibit organizations from using designated foreign intellectual property. If cross-border trade restrictions classify downstream technical updates, maintenance contributions, or commercial deployment as prohibited technical interactions with a restricted entity, a bank’s legal department must mandate the removal of those models.
How Does DORA Regulate Bank Software Supply Chains?
Under European banking supervision, operational resilience rules govern internal software pipelines just as strictly as cross-border trade statutes. The European Union’s Digital Operational Resilience Act (DORA) enforces oversight over Information and Communication Technology (ICT) supply chains under Articles 28 through 30.
National supervisory bodies, including the European Central Bank (ECB), the United Kingdom’s Prudential Regulation Authority (PRA), and the Financial Conduct Authority (FCA), retain authority to inspect the auditability and provenance of banking infrastructure tools. When an enterprise software assistant generates logic for payment processing systems, customer verification modules, or accounting ledgers, financial examiners assess the security of that toolchain.
Under Articles 28–30 of DORA, supervisors can demand verifiable audit records and defined exit strategies for software dependencies. When an institution cannot independently examine pre-training corpora, safety alignment criteria, or sovereign state influence behind a model family, financial authorities possess the statutory power to order the decommissioning of that model from core workflows.
What Does a Forced AI “Rip-and-Replace” Actually Cost a Fintech?
Evaluating open-weight models strictly by raw inference pricing obscures the potential financial liability of an emergency code migration. In an operational presentation, digital bank Revolut Ltd. noted that self-hosting Zhipu AI’s GLM-5.3 on a dedicated cluster of 56 Nvidia B200 GPUs brought developer token expenditures down to approximately 30 cents per million tokens, cutting API costs by 90%.
That operating ledger excludes the unhedged capital cost of replacing the tool under regulatory scrutiny. When a company deploying 2,000 engineers is required to discontinue an internal foundation model, the disruption goes beyond buying different server hardware:
- Engineering teams divert working hours from commercial product development to prompt migration, model validation, and automated code-generation testing.
- Developer output declines as staff recalibrate internal pipelines to account for differing model hallucinations and token vocabularies.
- Platform infrastructure teams must finance parallel compute clusters during multi-month security audits to preserve system uptime.
For an enterprise engineering organization with 2,000 developers, standard industry payroll rates mean a three-to-six-month refactoring cycle diverts tens of millions of dollars in developer salaries toward platform stabilization. A single mandatory compliance refactor can erase years of marginal token savings.
Frequently Asked Questions
What are the primary risks of Chinese AI models in banking? The main risks involve regulatory intervention under ICT resilience laws like the EU’s DORA, potential trade sanctions on foreign software IP, and engineering dependencies. If financial authorities decide an institution cannot properly audit a model’s origin, the bank must remove the system from its developer workflow.
Does self-hosting open-weight models protect banks from data privacy breaches? Self-hosting static model weights in a private Virtual Private Cloud (VPC) prevents customer records from transmitting to overseas servers. However, it does not shield the institution from supply-chain compliance rules, intellectual property disputes, or sovereign software audit requirements.
How does the EU Digital Operational Resilience Act apply to coding assistants? DORA Articles 28–30 govern third-party ICT service arrangements and subcontracting chains across financial institutions. When internal tools write or test code deployed to production banking systems, supervisors can review the provenance and security risks of those systems.
Why is replacing an open-weight foundation model difficult for a large bank? Organizations build internal scaffolding around specific model families, including prompt libraries, context-window optimizations, and automated test-generation suites. Migrating to an alternative open model requires extensive regression testing, system re-prompting, and developer workflow retraining across all engineering teams.

Praseetha K
Praseetha K is the Managing Editor of Clarity Times. She edits, verifies and publishes the newsroom's articles, and also writes analysis on policy, law, business and technology. Articles she writes are edited by the Editor-in-Chief before publication.